Eleven Agents in the Background
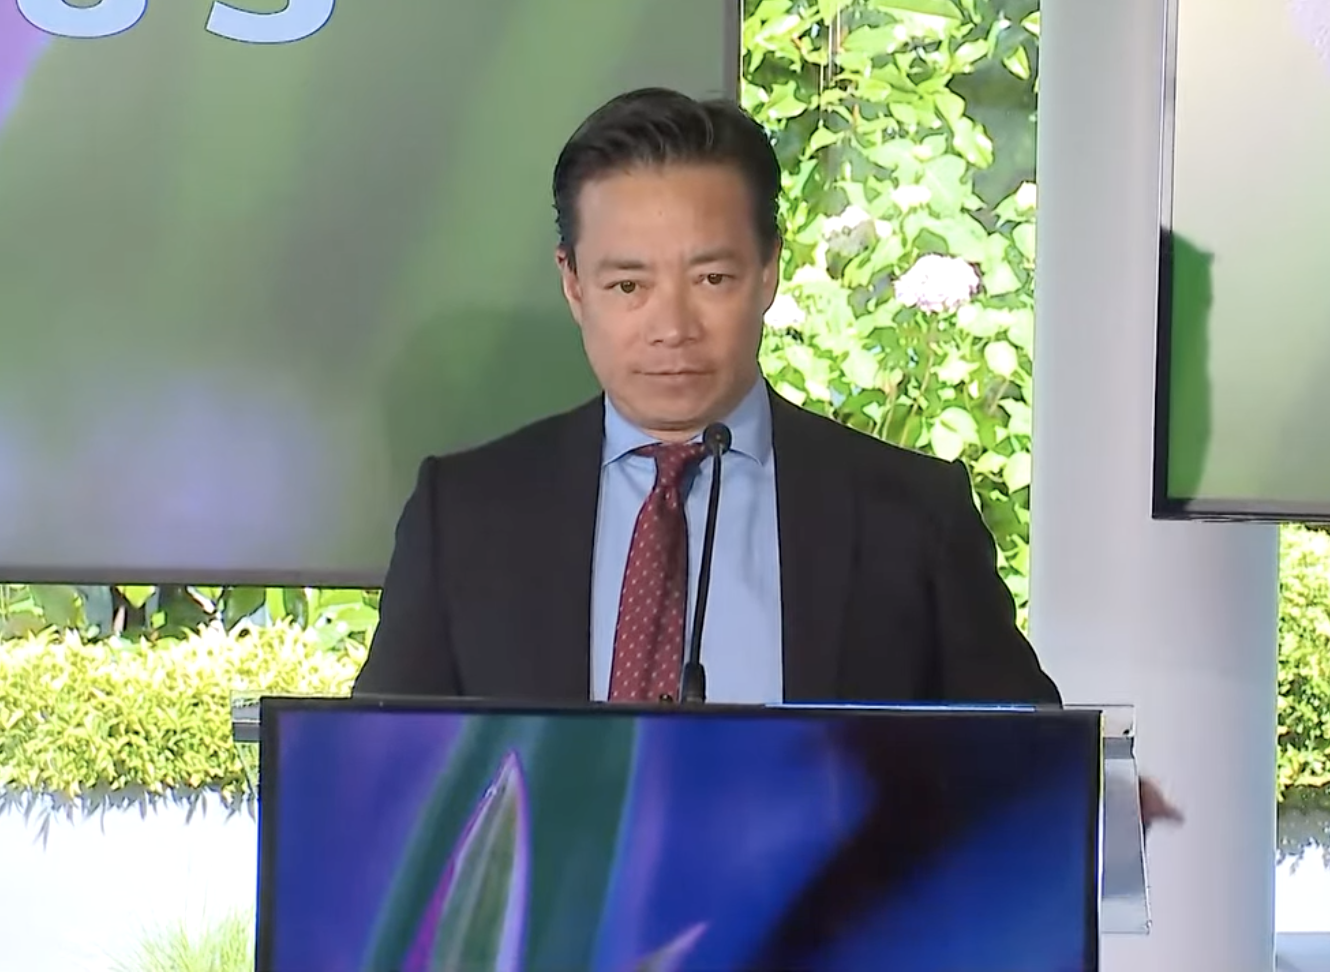
“AI is doubling every 5 months. AI will be 64 times better in 3 years. Think of ChatGPT, think of OpenClaw, think of Claude Code - 64 times better. I’m running a bunch of AI. I have 11 AI agents running right now, doing all my - a lot of my work in the background.” - Vancouver Mayor Ken Sim, May 2026
Context
This statement was made by Mayor Sim at the announcement of Canada’s sovereign AI data centre partnership between the federal government and Telus - a $9 billion investment in Canadian AI infrastructure attended by federal ministers and provincial representatives. Sim was speaking in support of the investment, which he described as “nation building” and “critical national infrastructure.” In the same speech, he named the tools he personally uses: ChatGPT (OpenAI, US infrastructure), OpenClaw (open-source autonomous agent, processes through commercial AI APIs on US infrastructure), and Claude Code (Anthropic, US infrastructure). He did not appear to recognise that his own AI use represents precisely the sovereignty gap the investment he was endorsing is designed to close.
This situation illustrates a structural reality beyond a Mayor naming worrisome AI risk vectors when appearing to speak off-script about his heavy dependence on agentic AI to do his job. And the reality is this today in Canada: even leaders who understand the national strategic case for sovereign AI do not yet have access to practical Canadian alternatives for the day-to-day AI tools they reach for, because no enterprise AI provider offers a solution safe from the US CLOUD act.
The $9 billion Telus investment, Microsoft’s Canadian sovereign AI commitments, and the Sovereign AI Landing Zone are all designed to address this gap - but none of them are operational yet for everyday use.
Unless a municipality is hosting his own LLM in a Canadian data center, the mayor’s eleven agents run on the very US infrastructure that Canada is spending billions to replace. That gap, between the sovereign AI future Canada is building and the US-dependent present Canadians are living in, is the governance problem this document analyses.
Executive Summary
At a federal government event announcing $9 billion in Canadian sovereign AI infrastructure, attended by ministers and designed to reduce Canada’s dependence on US-based AI systems, Vancouver Mayor Ken Sim stepped to the microphone and casually mentioned that he personally runs eleven AI agents in the background of his mayoral office - and named the tools: ChatGPT, OpenClaw, and Claude Code, all operating on US commercial infrastructure. He did not appear to notice the contradiction. This document explains why that moment matters, and why it is almost certainly not an isolated problem. Under BC’s Freedom of Information and Protection of Privacy Act, every AI deployment that processes personal information in a public body requires a Privacy Impact Assessment completed before it goes live, a documented cross-border risk assessment if it runs on US infrastructure, and mandatory breach notification if something goes wrong. None of these requirements have been publicly disclosed for the mayor’s eleven agents. The commercial tools he named process data on US servers and are reachable by US authorities under the CLOUD Act regardless of where the data is stored. That means the email a transgender Vancouverite sent about a housing concern, the message a Ukrainian Canadian sent about a community event, the inquiry from a US person who accessed healthcare in Canada: all of it may be flowing through infrastructure a foreign government can legally compel to produce records, with no notice to the individual and no disclosed risk assessment in place.
The broader problem is that the mayor’s eleven agents are likely the most visible tip of a much larger ungoverned AI footprint. City employees installing GitHub Copilot on work machines while writing scripts that touch city data, or deploying OpenClaw - an agentic AI tool with full local filesystem access, shell execution, and documented vulnerabilities flagged by Cisco - are creating the same FOIPPA exposure without any of the visibility. Sim was right about one thing: the sovereign AI infrastructure Canada is building matters enormously. It matters precisely because the tools in daily use today, including the ones he named, route Canadian government data through US systems and leave it exposed to US legal process. The $9 billion investment is the long-term solution. Responsible governance practice is what fills the gap while that infrastructure is built. What that looks like - tiered data handling, human review checkpoints, Privacy Impact Assessments, audit trails, and a framework that holds under public scrutiny - is documented in the pages that follow. Organizations ready to move from exposure to confidence can start with a structured readiness assessment; RO IT Systems specializes in exactly that work for regulated and public-interest environments, with reduced rates for municipalities and nonprofits.
Conclusion
The Mayor of Vancouver’s acknowledged reliance on eleven US-based AI agents, including ChatGPT, OpenClaw, and Claude Code, directly exposes a critical governance gap: the city is at risk of operating outside the foundational requirements of the BC Freedom of Information and Protection of Privacy Act (FOIPPA). As disclosed, these deployments appear to lack the mandatory pre-deployment Privacy Impact Assessments (PIAs) and cross-border risk assessments required for systems running on US commercial infrastructure, which is subject to the US CLOUD Act. This situation creates a foreseeable risk of harm, particularly for vulnerable residents whose sensitive personal information could be subject to access by a foreign government. Moving from this ‘ungoverned’ state to a defensible position requires demonstrating compliance with FOIPPA through public disclosure, documented assessment, auditable records, and a robust human review layer before any AI-assisted action becomes official city business.
How to Read This Document
This document mixes three distinct types of claim. Readers should know which is which.
📋 Existing Law identifies statutory requirements currently in force. These are not recommendations. They are legal obligations that apply to BC public bodies right now, with enforcement mechanisms and penalties attached. The relevant statutes are cited throughout.
⚠️ Accountability identifies gaps between existing law and the disclosed facts about Mayor Sim’s AI deployments. These are the questions that flow from existing obligations and that a regulator, journalist, or opposition official could legitimately pursue.
💡 Best Practice identifies recommended approaches that go beyond what the law strictly requires. These represent sound governance, responsible AI deployment, and the standard that well-run public sector organizations are moving toward. They are not legally mandated unless specifically noted.
Where a section or claim falls is marked at the relevant point. If a passage is not marked, it is factual or analytical context rather than a normative claim.
BC’s Privacy Law Framework
Why This Matters Before Anything Else
BC has a layered privacy law framework. Understanding which law applies, and to whom, is essential before evaluating any AI deployment in a public official’s office. Three statutes are directly relevant here.
flowchart TD
subgraph BC ["BC Privacy Law Framework"]
FOIPPA["FOIPPA 1993<br/>Freedom of Information<br/>and Protection of Privacy Act<br/>Public sector"]
PIPA["PIPA 2004<br/>Personal Information<br/>Protection Act<br/>Private sector"]
PA["BC Privacy Act<br/>Statutory tort of<br/>privacy violation"]
end
subgraph US ["US Federal Law - Extraterritorial Reach"]
CLOUD["CLOUD Act 2018<br/>Compels US companies to produce<br/>customer data anywhere in the world<br/>including Canada"]
end
FOIPPA --> PB["City of Vancouver<br/>All BC municipalities<br/>Health authorities · School boards<br/>Crown corporations<br/>2,900+ public bodies"]
PIPA --> PS["AI Vendors operating in BC<br/>OpenAI · Anthropic · Google · Microsoft<br/>Private sector data processors"]
PA --> IND["Any person in BC<br/>who wilfully violates<br/>another's privacy"]
CLOUD --> USC["Every major AI provider<br/>including those with<br/>Canadian data centres"]
PB -.->|"FOIPPA obligations<br/>follow city data<br/>to vendors"| PS
USC -.->|"Overrides Canadian<br/>data residency<br/>for US authorities"| PS
style FOIPPA fill:#74c0fc,color:#111827
style PIPA fill:#a9e34b,color:#111827
style PA fill:#ffd43b,color:#111827
style CLOUD fill:#ff6b6b,color:#fff
style USC fill:#ff6b6b,color:#fff
style BC fill:#f8f9fa,stroke:#868e96
style US fill:#fff5f5,stroke:#c92a2a
FOIPPA: The Public Sector Law
British Columbia’s Freedom of Information and Protection of Privacy Act (FOIPPA), in force since 1993, governs how public bodies in BC collect, use, store, and disclose personal information. It applies to more than 2,900 public bodies in the province, including every municipality, school board, health authority, and Crown corporation. The City of Vancouver is a public body under FOIPPA. So is every department within it.
FOIPPA exists for two related but distinct reasons.
The first is accountability. Before FOIPPA, government held information about its own operations without any legal obligation to share it with the public. The Act created a right of access: any person can request records in the custody or control of a public body, and the public body must respond. This is the freedom of information half of the law, the mechanism by which journalists, researchers, opposition politicians, and ordinary citizens can see what government is actually doing.
The second is privacy protection. Government collects personal information about people constantly, through tax filings, permit applications, social services, court records, licensing, and the ordinary business of governing. Before FOIPPA, there were no binding rules about what government could do with that information once it had it. The Act created those rules: personal information can only be collected for a lawful purpose, used for the purpose it was collected, and disclosed only in defined circumstances. It also gave individuals the right to access their own personal information held by government and to request corrections.
Together, these two halves of the law encode a basic democratic principle: government is accountable to the people it serves, and the people it serves have a right to control information about themselves.
Rather than prohibiting AI, FOIPPA requires that it be adequately governed: that its use be assessed before deployment, that personal information be handled lawfully, that records be kept, and that the public retain the ability to know what government is doing with information about them.
PIPA: The Private Sector Law
BC’s Personal Information Protection Act (PIPA), in force since 2004, governs how private sector organizations operating in BC handle personal information. BC is one of only three provinces with privacy legislation deemed substantially similar to the federal standard, which means PIPA applies in place of federal law for most provincially regulated activity. PIPA does not apply to public bodies - that is FOIPPA’s domain exclusively.
PIPA is relevant to the Sim AI story in one specific way: it governs AI vendors in their general commercial activities with BC residents. OpenAI, Anthropic, Google, and Microsoft are private sector organizations. In their day-to-day commercial dealings involving BC residents’ personal information, PIPA’s requirements apply to them.
However, when those same vendors are acting as service providers processing personal information on behalf of the City of Vancouver, a different legal instrument takes over. Bill 22 (2021) explicitly extended FOIPPA’s personal information protection requirements to service providers and their employees when processing personal information on behalf of a public body. In this relationship, it is FOIPPA that binds the vendor, not PIPA. The public body - the city - remains responsible for ensuring its service providers comply, and cannot contract out of those obligations.
This distinction matters for the Sim AI question in a specific way. If Mayor Sim is using city-issued enterprise accounts, the vendors are service providers under FOIPPA and the city has contractual and legal obligations to ensure they meet FOIPPA standards. If he is using personal consumer accounts, those accounts are outside the city’s FOIPPA framework entirely, the vendors have no service provider agreement with the city, and the personal information flowing through those accounts has no FOIPPA protection in that relationship at all. Consumer accounts are governed only by the vendor’s terms of service and, in general commercial terms, by PIPA - a significantly weaker protection for city records.
Both FOIPPA and PIPA are administered by the Office of the Information and Privacy Commissioner for BC (OIPC). The same commissioner who oversees public body compliance also has jurisdiction over private sector organizations operating in the province.
The BC Privacy Act
BC’s Privacy Act creates a statutory tort: a person who violates the privacy of another is liable to that person in damages. Unlike FOIPPA and PIPA, which are regulatory regimes, the Privacy Act gives individuals a direct cause of action in court. It is rarely litigated but it exists, and it applies to any person, including government officials, who wilfully violates another’s privacy in BC.
The CLOUD Act Problem
The more pressing cross-border concern is not Canadian law but American. The US Clarifying Lawful Overseas Use of Data Act (CLOUD Act, 2018) allows US government authorities to compel US-based companies to produce data held anywhere in the world, including in Canada. Every major commercial AI provider, including those with Canadian data centres, is a US company subject to the CLOUD Act. This means personal information processed by these systems, even if stored in Canada, is potentially reachable by US authorities without notice to the individual or the Canadian public body. This risk must be assessed and documented in any FOIPPA-compliant Privacy Impact Assessment for cross-border AI processing.
Part One: The Regulatory Requirements
FOIPPA Obligations for AI Deployments
The City of Vancouver is a public body under FOIPPA. That classification means every program or initiative that processes personal information, including AI agents operating in the mayor’s office, carries legal obligations that do not apply to private executives doing the same thing.
The tools Mayor Sim named in his verified public statement - ChatGPT (OpenAI), OpenClaw, and Claude Code (Anthropic) - are all commercial AI products running on US-based infrastructure. None of them are Canadian sovereign AI products. All of them process prompts on US servers. All of the companies behind them are subject to the US CLOUD Act. This is not an inference about what tools he might be using. It is a matter of public record, stated by the mayor himself at a federal government event.
📋 Existing Law - Privacy Impact Assessments are mandatory, not advisory.
Under s.69 of FOIPPA as amended by Bill 22 (2021), all BC public bodies must conduct Privacy Impact Assessments on new programs and initiatives before deployment. This is statute, not best practice guidance. The amendment came into force November 25, 2021. Penalties for breaches (including collecting personal information without authorization) were increased to up to $50,000.
The mayor’s inbox contains constituent personal information by definition. Housing situations, financial hardship, health disclosures, casework details: all of it flows through mayoral correspondence. AI agents processing that correspondence are processing personal information. A PIA was legally required before those agents went live.
📋 Existing Law - Cross-border processing triggers an additional mandatory assessment.
The Bill 22 amendments permit public bodies to process personal information outside Canada, but only with a documented risk assessment conducted within the PIA. This assessment must address the sensitivity of the data, the likelihood of foreign government access, and the contractual and technical mitigations in place. This is not optional even where the overall PIA is otherwise complete.
Any commercial AI infrastructure (OpenAI, Anthropic, Google, Microsoft Azure outside Canadian region) processes prompts on US-based infrastructure. The US CLOUD Act allows US authorities to compel US companies to produce data regardless of where it is physically stored. Microsoft, in its December 2025 Canadian commitment, pledged to challenge such demands where it has legal grounds. That is a commitment to contest, not a guarantee of success. For sensitive government correspondence, the distinction matters.
📋 Existing Law - Mandatory privacy breach notification is now in force.
As of February 1, 2023, all BC public bodies must have a privacy management program and must notify the Information and Privacy Commissioner of any breach that could reasonably be expected to result in significant harm. If constituent personal information has already flowed through undisclosed AI agents on unvetted infrastructure, a reportable breach may have already occurred.
The City’s Own AI Governance Architecture
Existing City Policy (not statute) - The City of Vancouver has established its own AI Advisory Committee (AIAC), with representation from Risk, Equity, Privacy, Legal, Indigenous Relations, Finance, Human Resources and Technology Services. The city has publicly aligned its AI adoption with the Government of Canada’s Responsible AI standards.
An important clarification for public statements. The AIAC is an internal staff governance body. Vancouver’s records management policy explicitly notes that it applies to city departments and bodies but does not include Council or its committees. Whether the AIAC’s mandate formally extends to the mayor’s personal AI tool deployments is legally ambiguous.
📋 Existing Law - FOIPPA applies to the City of Vancouver as a public body regardless of which official generates the records. Mayoral correspondence is subject to FOI requests. AI-generated outputs that influence mayoral decisions are city records under FOIPPA and Vancouver’s Records Management By-law (VanRIMS). If those outputs are not being retained as such, the city is in breach of its records obligations.
The Ombudsperson’s Active Scrutiny
⚠️ Accountability - BC Ombudsperson Jay Chalke devoted specific attention to municipal AI in his 2024-25 annual report, noting that communities are increasingly encountering automated or AI-assisted decisions, including in municipal building permits. His central accountability question:
“Were humans in the loop? How was the decision made?”
Vancouver already leads all BC municipalities in Ombudsperson complaints, with 57 complaints in 2024-25, more than any other municipality in the province. The Ombudsperson has also called on the province to introduce enforceable ethics and integrity oversight for local officials, citing two recent Vancouver integrity reports as evidence of the gap.
“In the background” is the structural opposite of humans in the loop.
Part Two: The Compliance Decision Tree
📋 Existing Law / ⚠️ Accountability - Before evaluating specific architectures, every AI agent deployment in a public body should clear this decision path. The branch conditions marked in red reflect existing statutory requirements under FOIPPA. The orange branches reflect accountability gaps where existing law creates obligations not yet satisfied by the disclosed facts. The decision tree is not a best practice framework: it maps what the law requires.
flowchart TD
Start([AI Agent Deployment<br/>in Mayor's Office]) --> Q1{Does it process<br/>personal information?}
Q1 -->|No| Low[Lower risk path<br/>Document use case<br/>Notify IT Security<br/>Retain outputs as records]
Q1 -->|Yes| Q2{PIA completed<br/>before deployment?}
Q2 -->|No| Breach1[⚠️ FOIPPA Breach<br/>S.69 violation<br/>Up to $50,000 penalty<br/>Immediate remediation required]
Q2 -->|Yes| Q3{Data processed<br/>outside Canada?}
Q3 -->|Yes| Q4{Cross-border sensitive<br/>PI assessment completed<br/>within PIA?}
Q4 -->|No| Breach2[⚠️ Bill 22 Breach<br/>Additional FOIPPA<br/>requirement not met]
Q4 -->|Yes| Q5
Q3 -->|No| Q5{Human review layer<br/>before agent outputs<br/>become official actions?}
Q5 -->|No| Risk1[⚠️ Ombudsperson Risk<br/>Democratic accountability gap<br/>Fair process cannot be demonstrated]
Q5 -->|Yes| Q6{AI outputs retained<br/>as city records under<br/>VanRIMS?}
Q6 -->|No| Risk2[⚠️ Records Management<br/>Breach<br/>FOI obligations not met]
Q6 -->|Yes| Q7{CLOUD Act or foreign<br/>government access risk<br/>assessed and mitigated?}
Q7 -->|No| Risk3[⚠️ Residual sovereignty<br/>risk undocumented]
Q7 -->|Yes| Compliant([✅ Compliant Architecture<br/>Maintain documentation<br/>Audit periodically])
style Breach1 fill:#ff6b6b,color:#fff
style Breach2 fill:#ff6b6b,color:#fff
style Risk1 fill:#ffa94d,color:#fff
style Risk2 fill:#ffa94d,color:#fff
style Risk3 fill:#ffd43b,color:#111827
style Compliant fill:#69db7c,color:#111827
style Low fill:#a9e34b,color:#111827
Part Three: Technical Architecture for Email Processing
What a Compliant Email Processing System Looks Like
💡 Best Practice - The architecture described in this section is not legally mandated in its specific form. It represents what responsible AI-assisted email processing looks like for a public official’s office, designed to satisfy the existing legal requirements in Part One while remaining operationally practical. Where individual elements touch existing law (solicitor-client privilege, records retention, lobbyist registry obligations), those are noted.
Mayor’s office email is among the most sensitive government data in a city. A single inbox on any given day may contain constituent casework with health or financial disclosures, solicitor-client privileged communications from city legal counsel, correspondence from registered lobbyists (which carries its own audit obligations under Vancouver’s lobbyist registry), intergovernmental correspondence with provincial or federal counterparts, and pre-decisional material subject to FOI.
These categories cannot be handled the same way. A compliant AI-assisted email processing system requires tiered handling before any LLM touches the content.
Email Tier Classification
| Tier | Category | AI Processing |
|---|---|---|
| 1 | Legal / Solicitor-Client Privileged | None. Flag to Chief of Staff only. |
| 2 | Constituent Casework (personal information) | Summarization with mandatory PII masking first |
| 3 | Registered Lobbyist Correspondence | Summarization plus automatic registry cross-check log |
| 4 | Intergovernmental | Summarization with mandatory human review before any action |
| 5 | Media / Public Inquiries | Full AI processing, lowest restriction |
| 6 | Internal Staff / Council | Summarization; standard retention rules apply |
The Four-Layer Architecture
flowchart TD
A([Mayor's Inbox<br/>M365 or equivalent<br/>Canadian tenancy]) --> B
B[Tier Classification Engine<br/>Rule-based · In-tenancy<br/>No LLM at this stage]
B --> C{Tier<br/>Assignment}
C -->|Tier 1: Legal| D([🚫 No AI Processing<br/>Direct flag to<br/>Chief of Staff])
C -->|Tiers 2-6| E[PII Masking Layer<br/>Names · Addresses · Health identifiers<br/>Financial data pseudonymized<br/>Original retained untouched]
E --> F[LLM Summarization<br/>Azure OpenAI - Canada region preferred<br/>or approved on-premise model<br/>Outputs structured brief only]
F --> G([Structured Brief<br/>Sender type · Tier · Priority flag<br/>Key issue · Two-sentence summary<br/>Suggested action category])
G --> H[Chief of Staff / EA<br/>Human Review Checkpoint<br/>Validates classification<br/>Approves or escalates]
H --> I([Mayor's Action Queue])
F --> J[(Audit Log<br/>Processing timestamp<br/>Model version<br/>Tier assigned<br/>Retained under VanRIMS)]
H --> J
I --> J
style D fill:#ff6b6b,color:#fff
style J fill:#74c0fc,color:#111827
style H fill:#b2f2bb,color:#111827
⚠️ Accountability - The human review checkpoint is non-negotiable. The AI output does not go directly to the mayor. It goes to a designated reviewer (chief of staff or executive assistant) who validates the summary, confirms the tier classification, and approves any action items before they become mayoral actions. This is what converts AI-assisted processing into a governable workflow. Without it, the Ombudsperson’s accountability standard cannot be met.
Part Four: Use Case Analysis
💡 Best Practice / 📋 Existing Law - The use cases below are analytical. Risk profiles represent best practice assessment of what responsible governance looks like. Where a compliance posture note references specific legal requirements (PIA, cross-border assessment, records retention), those elements are existing law, not recommendations.
Use Case 1: Single-Agent, Trigger-Based Processing
An event occurs (an email arrives, a document is uploaded, a calendar threshold is reached) and a single agent fires in response. The agent performs a defined, bounded task and produces a defined output. It then stops.
This is the most defensible agentic pattern. The scope of autonomous action is narrow. The data exposure is limited to the triggering input and the output. If that output sits in a queue for human review rather than triggering further autonomous action, the agent has assisted a human decision rather than made one.
sequenceDiagram
participant Email as 📧 Incoming Email
participant Trigger as Trigger System
participant Class as Classification Engine
participant PII as PII Masking Layer
participant Agent as Single Agent LLM
participant Queue as Output Queue
participant Human as 👤 Human Reviewer
participant Log as 📋 Audit Log
Email->>Trigger: Email received
Trigger->>Class: Fire with full payload
Class->>Class: Assign tier
alt Tier 1: Legal / Privileged
Class->>Human: Direct flag, no AI processing
else Tiers 2-6
Class->>PII: Pass email for masking
PII->>Agent: Masked payload
Agent->>Agent: Classify · Summarize · Flag
Agent->>Queue: Structured brief
Agent->>Log: Processing record + model version
Queue->>Human: Review prompt
Human->>Human: Validate · Escalate · Act
Human->>Log: Review timestamp + decision
end
Risk profile: Contained. Key failure modes are misclassification (a Tier 1 item processed as Tier 3), hallucination in the summary, and data exposure at the inference point. All are addressable with tiered pre-processing and human review. PIA scope is bounded and documentable.
Compliance posture: Requires PIA; cross-border assessment if inference happens outside Canada; output retention under VanRIMS. This is the architecture that a well-governed public sector AI deployment looks like.
Use Case 2: Inter-Agent Orchestration
An orchestrator agent receives a triggering event and coordinates multiple specialist agents. Each agent handles a different aspect of the task: constituent history, policy context, legal review, communications style. Agents pass information to each other. The orchestrator synthesizes outputs and produces a recommendation or action.
flowchart TD
Input([📧 Incoming Email]) --> Orch
Orch[Orchestrator Agent<br/>Routes task components<br/>Manages agent outputs]
Orch --> CA[Constituent<br/>History Agent<br/>Checks prior interactions]
Orch --> PA[Policy<br/>Knowledge Agent<br/>Retrieves relevant policy]
Orch --> LA[Legal<br/>Review Agent<br/>Flags privilege / risk]
Orch --> CSA[Communications<br/>Style Agent<br/>Drafts response framing]
CA -->|Personal information<br/>passed between agents| Synth
PA --> Synth
LA --> Synth
CSA --> Synth
Synth[Synthesis Layer<br/>Orchestrator aggregates<br/>specialist outputs]
Synth --> Rec([Recommendation<br/>or Draft Output])
Rec --> Human([👤 Human Review<br/>Mandatory])
subgraph risk [" ⚠️ Inter-Agent Risk Zone"]
CA
PA
LA
CSA
Synth
end
style LA fill:#ff9999
style risk fill:#fff3bf,stroke:#ffd43b,stroke-width:2px
style Human fill:#b2f2bb,color:#111827
This architecture is where the compliance picture becomes genuinely difficult.
Agent-to-agent communication is itself data processing. When the orchestrator passes constituent information to a specialist agent, that transfer is a data flow. If agents run as separate API calls (even to the same provider) each call is a discrete processing event. Personal information in a multi-agent chain may touch multiple containers, multiple jurisdictions, and multiple terms-of-service contexts in a single transaction. None of this is visible in the final output.
📋 Existing Law - The PIA problem is structural. A PIA for a single-agent system documents a bounded data flow. A PIA for an inter-agent system must document the full graph: every agent, every inter-agent communication path, every external tool or database the agents can access, and the cumulative data exposure across the chain. Under FOIPPA’s 2011 amendments, a multi-agent system processing constituent personal information likely qualifies as a “common or integrated program or activity,” which may require submission to the Office of the Information and Privacy Commissioner rather than just internal completion of a PIA.
💡 Best Practice - Prompt injection is an elevated, active threat. A malicious actor who knows the mayor’s office uses AI agents to process email can craft a message designed to exploit that. Instructions embedded in email text that look like normal correspondence to a human may be interpreted as commands by an agent with access to calendaring, file storage, or communication tools. In a single-agent system, the blast radius of a successful injection is limited. In a multi-agent system, an injected instruction can propagate across the agent network before any human sees the output.
⚠️ Accountability - Emergent behaviour cannot be audited after the fact. Individual agents behave as designed. Agents interacting with each other can produce outcomes neither was individually designed to produce. For government operations, emergent behaviour without documented human oversight is a direct failure of the Ombudsperson’s accountability standard and is nearly impossible to reconstruct if no inter-agent communication log exists.
Use Case 3: Shadow AI - Unsanctioned Employee Deployments
⚠️ Accountability / 📋 Existing Law - The two use cases above address AI deployed at the mayoral or senior administrative level. This use case addresses a different and in many ways harder problem: the AI that nobody approved, that IT Security never reviewed, and that is running right now on city workstations without a PIA, a vendor agreement, or a records management plan.
Shadow AI is the use of AI tools by employees outside the organization’s official procurement and governance processes. It is not a hypothetical risk in 2026. It is the default state of most organizations that have not implemented explicit controls. The barrier to installing a capable AI agent on a personal or city-issued machine is now trivially low, and the tools available are far more powerful than anything available to a public sector employee three years ago.
Two specific tools illustrate the range of risk.
GitHub Copilot in VS Code
GitHub Copilot is an AI coding assistant, made by Microsoft, that integrates directly into VS Code and other development environments. It is widely used by developers, IT administrators, and technical staff. Its function is to suggest and complete code as a developer types, drawing on the context of the file currently open and surrounding files in the workspace.
The governance risk is in what “context” means in practice. When a city IT employee writes a script to process a constituent database, query a permits system, or automate a records management task, Copilot sends that code context, including the surrounding files, variable names, database schemas, and any data literals present in the code, to GitHub’s servers for completion. If a connection string containing database credentials is in the file, it is in the context. If sample data from a constituent record was pasted in to test a script, it is in the context. If the script reads from a file containing personal information and that file path or schema is visible, it is in the context.
GitHub’s servers are Microsoft infrastructure. Microsoft is a US company subject to the CLOUD Act. Consumer and standard developer Copilot subscriptions do not offer the data processing agreements required for a FOIPPA-compliant service provider relationship. A city IT employee using a personal GitHub Copilot account on a city machine, while working on city data, has created a cross-border transfer of potentially sensitive information with no PIA, no vendor agreement, no audit log, and no legal basis under FOIPPA.
OpenClaw
OpenClaw is one of the three tools Mayor Sim named by name in his speech - the others being ChatGPT and Claude Code. It is an open-source autonomous AI agent that first appeared in late 2025 as Clawdbot, renamed following trademark concerns from Anthropic, and now has over 247,000 GitHub stars and an active international development community. It is designed to be installed on a local machine and given broad system access: it can read and write files, execute shell commands, send and receive email, control a browser, and connect to messaging platforms including WhatsApp, Telegram, Slack, Teams, and Discord.
The design intent is productivity. A person installs OpenClaw on their machine, connects it to their communication channels and local environment, and tasks it with autonomous work: clearing an email backlog, coordinating calendar entries, researching a topic, running background tasks on a cron schedule. It interacts with the user through messaging apps they already use, feels conversational, and operates continuously in the background.
The security profile for a city workstation is severe. Cisco’s AI security research team tested a third-party OpenClaw skill and found it performed data exfiltration and prompt injection without user awareness. One of OpenClaw’s own maintainers warned publicly that the tool is “far too dangerous for anyone who can’t understand how to run a command line to use safely.” There have been documented reports of agents deleting email inboxes during automated cleanup workflows. The Chinese government moved in March 2026 to restrict state agencies, state-owned enterprises, and banks from using the tool, citing unauthorized data deletion and leaks. Microsoft CEO Satya Nadella described OpenClaw in February 2026 as a “virus”-like security risk, even as Microsoft internally began building its own competing product.
For a municipal employee who installs OpenClaw on a city-issued workstation:
- The agent has access to every file on that machine, including any city records, constituent data, or internal documents stored locally
- The agent connects to the employee’s email, which may include city correspondence, constituent communications, and internal deliberations
- The agent makes API calls to commercial AI providers (LLM inference) using the employee’s own API key, creating an unaudited, undocumented cross-border data flow
- The agent can execute shell commands, meaning it can interact with city network resources, databases, or systems accessible from that machine
- Prompt injection through a malicious email or document could instruct the agent to exfiltrate data, make unauthorized changes, or take other actions the employee never intended
- None of this generates a record in any city system, satisfies any audit obligation, or appears in any compliance framework
flowchart TD
Employee(["👤 City Employee<br/>Installs AI tool<br/>without IT approval"])
subgraph Tools ["Shadow AI Tools on City Workstation"]
Copilot["GitHub Copilot in VS Code<br/>Sends code context to<br/>GitHub servers (US)<br/>Includes: schemas · credentials<br/>sample data · file contents"]
OC["OpenClaw Agent<br/>Full local filesystem access<br/>Shell command execution<br/>Email and calendar access<br/>Messaging platform connections"]
end
Employee --> Copilot
Employee --> OC
Copilot --> US1{{"🌐 Microsoft / GitHub<br/>US Infrastructure<br/>CLOUD Act applies<br/>No FOIPPA vendor agreement"}}
OC --> US2{{"🌐 Commercial LLM API<br/>(employee's personal key)<br/>US Infrastructure<br/>No PIA · No audit trail"}}
OC --> Local["Local file system<br/>City records · Constituent data<br/>Network shares · Credentials"]
US1 --> Risk1["⚠️ Unaudited cross-border<br/>transfer of city data<br/>FOIPPA breach"]
US2 --> Risk2["⚠️ Unaudited cross-border<br/>transfer of city data<br/>FOIPPA breach"]
Local --> Risk3["⚠️ Prompt injection<br/>could exfiltrate data<br/>or execute unauthorized<br/>commands on city network"]
style US1 fill:#ff6b6b,color:#fff,stroke:#c92a2a
style US2 fill:#ff6b6b,color:#fff,stroke:#c92a2a
style Risk1 fill:#ffa94d,color:#fff
style Risk2 fill:#ffa94d,color:#fff
style Risk3 fill:#ffa94d,color:#fff
style Tools fill:#fff3bf,stroke:#ffd43b,stroke-width:2px
Why this is harder to govern than sanctioned AI deployments
Sanctioned AI deployments have an accountable decision-maker, a procurement process, and at least the possibility of a PIA. Shadow AI has none of these entry points. An organization does not know what it has not been told about. The absence of disclosure is itself the governance failure, and it is not detectable through normal audit processes unless the organization has implemented monitoring tools specifically designed to identify unauthorised data flows from endpoints.
For a city administration that has publicly committed to responsible AI adoption through its AIAC framework, shadow AI deployments by staff represent a gap between the governance aspiration and the operational reality. The mayor’s statement that he runs eleven background agents may be the most visible instance of ungoverned AI in Vancouver city government. It is almost certainly not the only one.
📋 Existing Law - The obligations are the same regardless of whether the deployment is sanctioned or shadow. Any city employee whose use of an AI tool results in personal information leaving the city’s FOIPPA governance framework has created a potential breach. The city’s mandatory privacy management program (required since February 2023) is supposed to include controls sufficient to prevent and detect this. The gap between that requirement and the actual state of shadow AI in any organization of Vancouver’s size is a live compliance exposure that the AIAC’s current composition and scope must address.
Part Five: Deployment Architecture
Onboard vs. Internet-Based AI
📋 Existing Law / 💡 Best Practice - The cross-border assessment requirement in the table below is existing law under FOIPPA Bill 22. The remaining comparisons (model capability, infrastructure cost, vendor dependency, sovereign option) are analytical best practice considerations to inform decision-making, not legal requirements.
flowchart LR
subgraph Onboard ["🏢 Onboard / Resident AI: City-Controlled Infrastructure"]
direction TB
OI([Email Input]) --> OClass[Tier Classification]
OClass --> OPII[PII Masking]
OPII --> OModel[Local Model<br/>Llama · Mistral · Fine-tuned<br/>City data centre or<br/>Azure Canada private tenancy]
OModel --> OOut([Output])
OModel --> OLog[(Local Audit Log<br/>Full city control<br/>VanRIMS compliant)]
end
subgraph Internet ["☁️ Internet-Based AI: Commercial Infrastructure"]
direction TB
II([Email Input]) --> IClass[Tier Classification]
IClass --> IPII[PII Masking]
IPII --> Border{{"🌐 DATA LEAVES<br/>CANADIAN PERIMETER<br/>FOIPPA Cross-Border<br/>Assessment Required"}}
Border --> IModel[Commercial API<br/>OpenAI · Anthropic · Google<br/>US Infrastructure<br/>US CLOUD Act applies]
IModel --> IOut([Output])
IModel --> ILog[(Vendor Audit Log<br/>Partial visibility<br/>Contract-dependent)]
end
style Border fill:#ff6b6b,color:#fff,stroke:#c92a2a
style Onboard fill:#f0fff0,stroke:#2f9e44
style Internet fill:#fff5f5,stroke:#c92a2a
Risk and Compliance Comparison
| Dimension | Onboard / Resident | Internet-Based |
|---|---|---|
| FOIPPA cross-border assessment | Not required | Mandatory for sensitive PI |
| US CLOUD Act exposure | Not applicable | Applies regardless of data location |
| Audit trail control | Full, city controlled | Partial, vendor dependent |
| Model capability | Lower (open-weight models) | Higher (frontier commercial models) |
| Infrastructure cost | High | Low to moderate |
| Vendor dependency risk | None | Model deprecation, terms changes, outages |
| Training data risk | Controlled | Depends on agreement tier; consumer accounts have no protection |
| Deployment readiness (Canada) | Available now with investment | Available now; sovereignty gap until 2026+ |
| Canadian sovereign option | Optimal | Microsoft SAIL / in-country Copilot: 2026, timeline uncertain |
The Microsoft Copilot Reality Check
Microsoft’s Canadian sovereignty story is real but not yet complete. Two distinct capabilities are often conflated.
Data residency (storage) refers to where M365 tenant data lives at rest. This is available in Canadian data centres now for properly provisioned tenants.
In-country processing (inference) refers to where Copilot’s LLM actually runs prompts. This is not yet available in Canada. Microsoft announced it as coming in 2026 and updated in April 2026 that the timeline and scope are being refined. No firm delivery date is confirmed.
timeline
title Microsoft Canadian AI Sovereignty: What Is Available When
2021 : FOIPPA Bill 22 amendments in force
: Cross-border processing permitted with PIA assessment
2023 : Microsoft Azure Canada Central and East regions operational
: M365 data residency in Canada available
2025 Nov : Microsoft announces in-country Copilot processing for Canada
: 19B CAD investment commitment announced
2026 Apr : Microsoft updates timeline and scope under refinement
: No firm delivery date confirmed
2026 H2 : New Azure Canada capacity begins coming online
2026+ : Sovereign AI Landing Zone for Canada planned
: Full in-country Copilot inference date uncertain
Any commercial AI agent infrastructure in use in the mayor’s office today is almost certainly running inference outside Canada. The FOIPPA cross-border assessment is a legal requirement that must exist in a completed PIA before that processing began.
Part Six: The Full Risk Matrix
💡 Best Practice Analysis - The quadrant below synthesises the risk profiles from Parts Four and Five. It is an analytical framework, not a legal standard. The compliance obligations that apply at each quadrant (PIA, cross-border assessment, records retention) remain the same regardless of architecture. What changes is the complexity of meeting them.
quadrantChart
title Agentic AI Risk Profile by Architecture
x-axis "Single-Agent" --> "Multi-Agent / Inter-Agent"
y-axis "Onboard / Resident" --> "Internet-Based"
quadrant-1 Highest Risk
quadrant-2 High Risk
quadrant-3 Lowest Risk
quadrant-4 Moderate Risk
Single-Agent Onboard: [0.15, 0.2]
Multi-Agent Onboard: [0.75, 0.3]
Single-Agent Internet: [0.2, 0.75]
Multi-Agent Internet: [0.8, 0.85]
Single-Agent / Onboard: Lowest risk. PIA required but bounded. Full audit control. No cross-border exposure. Infrastructure investment required. Model capabilities limited.
Multi-Agent / Onboard: Moderate risk. PIA complex but data stays within controlled environment. Emergent behaviour and prompt injection risks exist but the audit trail is manageable. Better suited to internal-only data.
Single-Agent / Internet-Based: Moderate to high risk. PIA required plus cross-border assessment. Vendor dependency. CLOUD Act exposure. Audit trail depends on vendor logging. Manageable with a proper PIA and enterprise agreement protections.
Multi-Agent / Internet-Based: Highest risk. Multiple cross-border data flows per transaction. Inter-agent data graph difficult to document for PIA purposes. Prompt injection risk elevated and harder to contain. Audit trail fragmented across vendors. Emergent behaviour cannot be audited. The tools Mayor Sim named publicly - ChatGPT, OpenClaw, and Claude Code - all fall into this category. This is not inference. It is confirmed from the transcript of his public speech.
Part Seven: The Accountability Questions
These are the questions that any journalist, opposition councillor, FOI requestor, or advocacy organization can legitimately put to the mayor’s office. They are not hostile. They are the minimum transparency standard for a public official running AI agents on government business.
📋 Existing Law governs the compliance questions below. ⚠️ Accountability is what follows when those legal requirements have no disclosed answer.
On the tools (factual - prerequisite to assessing compliance):
- Which AI tools specifically constitute the “eleven agents”?
- Are these city-issued accounts under enterprise agreements, or personal consumer accounts?
- What tasks does each agent perform?
On compliance (📋 Existing Law - FOIPPA s.69, Bill 22, FOIPPA s.36.2-36.3):
- Have Privacy Impact Assessments been completed for each agent deployment?
- If personal information is processed, has the cross-border sensitive PI assessment been conducted within each PIA?
- Have these deployments been disclosed to the city’s IT Security function and reviewed?
- Has the city’s privacy management program (required under FOIPPA since February 2023) been applied to these deployments?
On records (📋 Existing Law - FOIPPA, VanRIMS Records Management By-law):
- Are AI-generated outputs (summaries, routing decisions, drafts) being retained as city records under VanRIMS?
- Are those outputs producible in response to FOI requests?
- Is a processing log (timestamps, model versions, inputs processed) being maintained?
On accountability (⚠️ Accountability - Ombudsperson standard, democratic obligation):
- Is there a human review layer before any agent output becomes an official mayoral action or communication?
- Is there a documented complaints pathway if a constituent’s correspondence is mishandled by an agent?
- Who is responsible for monitoring agent behaviour and identifying failures?
On sovereignty (📋 Existing Law - FOIPPA cross-border assessment / ⚠️ Accountability):
- On whose infrastructure are these agents running?
- If on US-based commercial infrastructure, has the CLOUD Act risk been assessed and documented?
- If on city-provisioned infrastructure, which data centre and under what contractual framework?
Part Eight: What Compliant Deployment Looks Like
💡 Best Practice (grounded in 📋 Existing Law) - The five conditions below are not a standalone best practice framework. Each one maps to a specific existing legal or accountability obligation: FOIPPA’s PIA requirement, the records management by-law, the Ombudsperson’s human-in-the-loop standard, FOIPPA’s right of access, and the cross-border assessment requirement. The framework synthesises those obligations into an operationally useful form.
The point of this analysis is not that AI agents in the mayor’s office are inherently wrong. Used transparently, with proper governance, they could make government more responsive. The point is that “in the background” describes the opposite of what responsible public sector AI deployment requires.
A compliant architecture satisfies five conditions.
flowchart LR
D(["1. Disclosed<br/>Public identification<br/>of AI tools in use<br/>and their purpose"])
A(["2. Assessed<br/>PIA completed before<br/>deployment · Cross-border<br/>assessment where needed"])
G(["3. Governed<br/>Human review layer<br/>between every agent<br/>output and official action"])
Au(["4. Auditable<br/>Processing logs · Output<br/>retention · Model versions<br/>all retained as city records"])
C(["5. Challengeable<br/>Clear complaints pathway<br/>for constituents whose<br/>correspondence is processed"])
D --> A --> G --> Au --> C
Fail(["⚠️ Current disclosed state:<br/>'Eleven agents in the background'<br/>satisfies none of these conditions"])
C -.->|"Gap"| Fail
style D fill:#b2f2bb,color:#111827
style A fill:#b2f2bb,color:#111827
style G fill:#b2f2bb,color:#111827
style Au fill:#b2f2bb,color:#111827
style C fill:#b2f2bb,color:#111827
style Fail fill:#ff6b6b,color:#fff
-
Disclosed. The city publicly identifies what AI tools are in use in the mayor’s office, for what purposes, and under what governance framework.
-
Assessed. A PIA exists for each deployment, completed before the tools went live, documenting data flows, legal authority, cross-border processing where applicable, and risk mitigations.
-
Governed. A human review layer sits between agent outputs and official mayoral actions. No agent output becomes a decision, communication, or action without human validation.
-
Auditable. Processing logs are maintained and retained as city records. AI-generated outputs are retained alongside original inputs. Model versions are recorded. The chain of custody for personal information is traceable.
-
Challengeable. Constituents whose correspondence is processed by AI have a clear pathway to understand how it was handled and to raise concerns if something went wrong.
The statement “eleven agents in the background” satisfies none of these conditions as disclosed. That gap (not the existence of the agents) is where the accountability question lives.
Part Nine: Protecting Vulnerable Canadians from Foreign Interference
The Data Sovereignty Risk Is Not Abstract
The compliance gaps in Mayor Sim’s AI deployment are not only bureaucratic concerns. For specific groups of Vancouverites, ungoverned AI processing of their interactions with city government creates a concrete risk of harm through the exposure of their personal information to foreign authorities. This section addresses two groups in particular: transgender and gender-diverse residents, and Canadian residents who hold US citizenship.
Fact Check: US Government and Transgender Classification
A note on precision before the analysis. The assertion that the US government has classified transgender persons as a terrorist organization is not accurate as stated, and a public statement should not reproduce it in that form.
What is documented and verifiable:
On January 20, 2025, President Trump signed an Executive Order titled “Defending Women from Gender Ideology Extremism and Restoring Biological Truth to the Federal Government,” which stripped federal recognition of gender identity and rescinded prior protections for transgender people. On September 25, 2025, Trump signed NSPM-7 (National Security Presidential Memorandum 7), “Countering Domestic Terrorism and Organized Political Violence,” which listed “extremism on migration, race, and gender” among indicators potentially associated with domestic terrorism. Civil liberties organizations including the ACLU have described this language as dangerously vague. In September 2025, the Heritage Foundation’s Oversight Project formally proposed that the FBI create a new domestic terrorism category called “Transgender Ideology-Inspired Violent Extremism” (TIVE). Independent reporting indicated the FBI was in developmental stages of such a classification. As of the time of writing, a formal FBI designation of transgender people as a terrorist category has not been confirmed as adopted policy, though the NSPM-7 language and FBI reporting create a credible and documented basis for concern.
Global Affairs Canada has issued a formal travel advisory warning Canadians who hold passports with an “X” gender marker that they may face additional scrutiny from US Customs and Border Protection. The Canadian Bar Association has formally called on Immigration, Refugees and Citizenship Canada to establish a dedicated immigration pathway for transgender individuals fleeing escalating risk in the United States.
The accurate framing for a public statement is: US federal policy and documented enforcement direction create a credible risk that gender identity information about Canadians could be of interest to US authorities, and that the CLOUD Act provides the legal mechanism by which US authorities could compel American AI companies to produce that information regardless of where it is stored.
Why This Connects to City Hall AI
📋 Existing Law - When a transgender Vancouverite contacts the mayor’s office about a housing concern, a discrimination complaint, or a request for service, they are sharing personal information with a public body. Under FOIPPA, that information is protected. Under the BC Human Rights Code, gender identity and gender expression are protected grounds. The city has an obligation not to discriminate on those grounds and to protect people’s rights in the delivery of services.
⚠️ Accountability - If that communication is processed by an AI agent running on US-based infrastructure, the CLOUD Act creates a legal pathway by which US authorities could compel the AI vendor to produce that data. The person who wrote to city hall to discuss their housing situation has no way to know their gender identity, their address, their circumstances, and their name may now be accessible to a foreign government that has classified advocacy for their rights as a potential terrorism indicator.
flowchart TD
Res(["🏳️⚧️ Transgender resident<br/>or dual citizen<br/>contacts mayor's office"])
Email["Email to Mayor's Office<br/>contains: name · address<br/>gender identity · circumstance"]
Agent["AI Agent<br/>commercial API<br/>no disclosed PIA"]
Res --> Email --> Agent
Agent --> Border{{"🌐 Data leaves<br/>Canadian perimeter<br/>for LLM inference"}}
Border --> USInfra["US AI Infrastructure<br/>OpenAI · Anthropic · Google<br/>US companies subject<br/>to CLOUD Act"]
USInfra --> CloudRisk["🇺🇸 CLOUD Act<br/>US authorities may compel<br/>production of this data<br/>without notice to Canada<br/>or the individual"]
CloudRisk --> Harm["⚠️ Foreseeable harm:<br/>gender identity · home address<br/>political activity · legal status<br/>exposed to foreign government<br/>that has flagged gender advocacy<br/>as potential terrorism indicator<br/>(NSPM-7, Sept 25 2025)"]
PIA["✅ FOIPPA requires:<br/>Sensitive PI cross-border<br/>assessment within PIA<br/>before this processing begins<br/>No such PIA disclosed"]
Agent -.->|"Required but<br/>not present"| PIA
style Border fill:#ff6b6b,color:#fff,stroke:#c92a2a
style CloudRisk fill:#ff6b6b,color:#fff
style Harm fill:#ffa94d,color:#fff
style PIA fill:#b2f2bb,color:#111827
style USInfra fill:#fff5f5,stroke:#c92a2a
This is not a hypothetical risk manufactured to inflate the stakes. It follows directly from three documented facts: NSPM-7's vague "gender extremism" language; the CLOUD Act's extraterritorial reach over US companies; and the absence of any disclosed PIA documenting how this risk has been assessed for the AI agents currently operating in the mayor's office.
Who Is Actually at Risk
The abstract language of data sovereignty becomes concrete when you consider who actually contacts a mayor’s office and what they disclose. The following are not edge cases. They are people who live in Vancouver now, who interact with city services, and who face specific, foreseeable harm if their communications are processed through AI infrastructure accessible to US authorities.
Persons supporting conflict in a third country. Vancouver has a significant Ukrainian diaspora community. Individuals who are fundraising for the Ukrainian resistance, coordinating humanitarian logistics, communicating with family members in active conflict zones, or engaged in advocacy work contact city government regularly. A single email to the mayor’s office about a community event permit or a business licence may contain names, addresses, organizational affiliations, and communications patterns that, in the hands of a hostile intelligence service or a foreign government aligned with Russia, could put people in Ukraine at risk. The CLOUD Act does not limit what US authorities do with data once they have it, nor what they share with whom under intelligence agreements.
US persons who accessed reproductive healthcare in Canada. Since the US Supreme Court’s Dobbs v. Jackson Women’s Health Organization decision in 2022, abortion is criminalized or severely restricted in more than a dozen US states. Some state attorneys general have signalled interest in prosecuting people who travel out of state to access abortion services. Canada has no such restrictions, and US persons regularly access reproductive healthcare here. A US person who contacted the mayor’s office, a city health service, or a community organization while in Vancouver, and whose communication was processed by US-based AI infrastructure, may have created a record accessible to US authorities connecting them to their presence in Canada during a period of healthcare access. The harm is direct and personal.
Transgender and gender-diverse persons with ties to or who have criticized the US. As documented earlier in this section, the Trump administration’s NSPM-7 (September 2025) uses language that civil liberties organizations say can be weaponized against gender advocacy. A transgender Vancouverite who has previously participated in US advocacy, publicly criticized US policy, donated to US trans rights organizations, or has family or organizational ties across the border is not simply a Canadian resident interacting with city government. They are a person whose identity, address, and activities could be of interest to US authorities under the current enforcement framework. Their email to the mayor about a neighbourhood concern is not political. But in the wrong hands, it is identifying information.
Canadians who fled persecution in the United States. Vancouver has received people who left the United States due to immigration status, political exposure, civil rights concerns, domestic safety, or the targeted nature of current federal enforcement. These people have deliberately separated themselves from US jurisdiction. They contact city services. They ask for help with housing, employment, or community services. If their communications pass through US-based AI infrastructure, the CLOUD Act creates a legal pathway back to the very authorities they fled. This is not a theoretical harm. For some people, it is the difference between safety and deportation, between anonymity and exposure.
The common thread is this: people who interact with their city government in good faith, disclosing personal circumstances to access services or participate in civic life, have a reasonable expectation that their information stays within Canada. An AI agent processing that communication on US infrastructure, without a disclosed PIA assessing this specific risk, violates that expectation with potentially life-altering consequences. This is not overclaiming. It is what the CLOUD Act permits, what NSPM-7’s language enables, and what the absence of a cross-border sensitive PI assessment leaves ungoverned.
The RF Dimension: When Communications Travel by Air
There is an additional exposure vector that applies when any of these communications occur over WiFi or other radio frequency transmission, rather than wired connection.
WiFi is radio. Every packet of data sent over a wireless network is a radio frequency transmission, physically present in the air and technically interceptable by anyone with the right equipment and proximity. This is not theoretical: the NSA’s STATEROOM program, revealed through documents leaked by Edward Snowden, is a documented signals intelligence collection operation run from US diplomatic missions in cities around the world, specifically targeting radio, telecommunications, and internet traffic in the surrounding area. The program is operated by the Special Collection Service, a joint NSA-CIA unit. Snowden documents confirm that SCS teams have conducted deliberate surveys of WiFi signals from nearby facilities in multiple cities, collecting communications from targets of interest in the immediate RF environment.
Vancouver hosts a US Consulate General at 1075 West Georgia Street, a US diplomatic facility. The STATEROOM program has been confirmed to operate from US embassies and consulates. No public disclosure confirms or denies whether STATEROOM or equivalent collection operates from the Vancouver consulate specifically. What is confirmed is that the program exists, that it targets WiFi among other signals, and that it operates from facilities of exactly this type in cities around the world.
For a vulnerable person submitting a communication to the mayor’s office over public or home WiFi, or for a city employee processing constituent correspondence wirelessly, the CLOUD Act exposure and the RF interception risk are parallel, not sequential. The data does not need to cross a border through a commercial AI vendor to be accessible to US intelligence. If the transmission itself travels through the air within range of collection equipment, it may already be collected at the point of origin, before it ever reaches a city server or an AI agent.
This is not an argument for alarm. It is an argument for candour about the environment in which Vancouver’s AI governance gap exists. The city’s failure to disclose, assess, and govern its AI deployments does not only create legal exposure under FOIPPA. For the most vulnerable people who contact city government, it leaves them unprotected in an environment where multiple vectors of foreign intelligence access exist, some of which are documented and some of which are not.
The BC Human Rights Code Obligation
📋 Existing Law - Under BC’s Human Rights Code, gender identity and expression are protected grounds. The code requires that service providers, including public bodies, not discriminate on those grounds. Where accommodation is required, the duty to accommodate applies unless it would cause undue hardship, a high threshold assessed against cost, health, and safety factors.
⚠️ Accountability - The situation described here is distinct from an accommodation question. Exposing a transgender resident’s gender identity to a foreign government through inadequately governed AI infrastructure is not a failure to accommodate. It is a failure to protect a person in a protected class from foreseeable harm in the delivery of a city service. The BC Human Rights Code prohibits discrimination in the provision of services and facilities customarily available to the public. Processing a constituent’s communication through infrastructure that foreseeably exposes their protected characteristics to a foreign authority is a service delivery failure with human rights implications, regardless of intent.
The Ontario Human Rights Commission’s AI impact assessment framework (the closest comparable guidance to what BC’s OIPC is now developing under its 2025-28 Strategic Plan) states explicitly that AI testing must consider gender differences, and that if different populations have not been considered in AI deployment design, the organization may be in violation of human rights obligations. The OIPC BC has committed to establishing a dedicated team focused on AI-related risks as part of its 2025-28 strategic plan. That regulatory attention is relevant context for any public body deploying AI that touches protected characteristics.
The Prudent Standard
Before deploying AI agents to process constituent communication or personal information, a public instution such as a municipality needs to assess whether the software creates differential risk for people with protected characteristics. This is human rights obligation. A transgender resident, a dual citizen, a person with an immigration-adjacent concern: these are not edge cases. They are the people a Human Rights statutes and the Canadian Charter of Rights and Freedoms are designed to protect, and they are the people most harmed when governance fails in our public institutions,
Part Ten: What a Prudent City of Vancouver Would Actually Do
💡 Best Practice - Everything in this section is recommended practice, not existing legal requirement. The recommendations are designed to satisfy the existing law described in Parts One and Nine, but the specific approaches, sequencing, and engagement formats described below go beyond what statute mandates. They represent what responsible public sector AI governance looks like in organisations that have done this well.
The accountability questions in Part Seven describe what is missing. This section is an example of what responsible AI deployment in a city administration looks like when done well, and what kind of work gets an organization from ungoverned to ready.
flowchart LR
R["🔍 AI Readiness<br/>Assessment<br/>2 days<br/>Prioritise use cases<br/>map readiness gaps<br/>90-day action plan"]
G["🏛️ Governance<br/>Design<br/>5 days<br/>Decision rights · PIA<br/>pathways · approval<br/>workflows · audit<br/>protocols"]
T["🎓 Safe AI Use<br/>Training<br/>2 days<br/>Shared staff rules<br/>ovtrust prevention<br/>escalation paths"]
I["⚙️ Integration<br/>Architecture<br/>5 days<br/>Tiered classification<br/>PII masking · audit<br/>logging · human<br/>review checkpoints"]
E["📋 Executive<br/>Briefing<br/>3 days<br/>Public-facing clarity<br/>accountability answers<br/>decision memos for<br/>elected officials"]
R --> G --> T --> I --> E
Outcome(["✅ City can answer<br/>every question in<br/>Part Seven directly<br/>and publicly"])
E --> Outcome
style R fill:#74c0fc,color:#111827
style G fill:#74c0fc,color:#111827
style T fill:#74c0fc,color:#111827
style I fill:#74c0fc,color:#111827
style E fill:#74c0fc,color:#111827
style Outcome fill:#b2f2bb,color:#111827
Start with Readiness, Not Tools
The most common mistake in public sector AI adoption is beginning with the tool and building governance around it afterward. The prudent starting point is the reverse: assess what the organization is actually ready for before any agent goes live.
The most common mistake in public sector AI adoption is beginning with the tool and building governance around it afterward. The prudent starting point is the reverse: assess what the organization is actually ready for before any agent goes live.
A structured AI readiness assessment typically takes two days and produces something concrete: prioritised use cases, readiness gaps mapped against them, and a 90-day action plan that sequences what to do in what order. For a city administration, this means identifying which workflows genuinely benefit from AI assistance, which carry unacceptable data exposure, and what infrastructure and governance conditions need to be in place before deployment begins. That kind of scoped, structured triage is the difference between a pilot that holds up under scrutiny and one that produces a quote like “eleven agents in the background.”
Governance Before Scale
Governance designed after AI is deployed is remediation. Governance designed before deployment is an accelerant, because it removes the friction of undocumented decisions and reduces the rework that comes from discovering problems in production.
For Vancouver specifically, governance work for an AI deployment would need to produce: documented decision rights (who approves what before an agent goes live), a review path for PIAs and cross-border assessments, audit documentation covering model versions and data flows, and a human review protocol that satisfies the Ombudsperson standard. This is not paper-heavy bureaucracy. Done well, it is a five-day engagement that produces a governance model, risk criteria, approval workflow, and audit-ready documentation the city can stand behind publicly.
The value of getting this right before a public statement is that the mayor can answer the accountability questions in Part Seven directly, confidently, and completely.
Safe AI Use Training Before Broad Deployment
The weakest link in many AI deployments is the human who uses it without understanding what it is doing with their data, when to trust its outputs, and when to escalate for human review. For a mayor’s office processing sensitive constituent correspondence, the consequences of overtrust are immediate and serious.
Safe AI use training establishes shared rules before scaling: what kinds of information should not enter an AI workflow, how to review outputs critically, when AI-assisted summaries require human verification before action, and what to do when something goes wrong. For city staff supporting the mayor, this kind of training is a foundation, not an optional add-on.
Architecture That Connects Insight to Action Safely
The topology described in Part Three of this document (tiered classification, PII masking, structured output, human review, audit logging) is not especially complex to design. What makes it hard is integrating it with existing systems, getting the data flows right, and building it so that the audit trail is automatically maintained rather than manually reconstructed.
Cities that have done this well have invested in the integration architecture that connects AI output to operational action through controlled, documented pathways. The integration problem is not new: connecting systems to produce business action has been a core enterprise technology challenge for decades. What is new is that the action-triggering component is now an AI agent, and the governance requirements around it are more demanding. Organizations with deep experience in production API design, ETL pipelines, and high-availability systems integration are particularly well-placed to design this kind of architecture, because the reliability and control disciplines transfer directly.
Board and Executive Clarity
For elected officials and senior administrators, the most practical investment before any AI deployment touches constituent data is an executive briefing that frames the decisions, risks, and language they need to answer public questions confidently. Not a slide deck describing what AI is, but a decision memo: here are the choices, here are the tradeoffs, here is what we need to decide, and here is what we can say publicly when we are asked.
Vancouver’s AIAC structure provides an internal governance layer. What it does not automatically provide is the external-facing clarity that allows an elected official to answer “which agents, on whose infrastructure, under what governance” without hesitation. That preparation is a distinct piece of work, and it is the piece that was visibly missing when the mayor made his statement.
A Note on Who Does This Work
Organizations navigating AI governance in regulated, public-sector, or high-stakes environments benefit from advisors who understand both the technical architecture and the compliance obligations, and who have worked in environments where the cost of getting it wrong is real. Financial services, utilities, aviation, and public-interest technology are the sectors that built the disciplines now being applied to AI governance: confidentiality, integrity, availability, audit trails, and real operational control.
Firms with that kind of cross-sector technical and governance depth, particularly those with established BC roots and public-interest experience, are the right conversation for a city administration that wants to move from “eleven agents in the background” to an AI programme it can defend publicly and stand behind legally.
RO IT Systems (roitsystems.ca) works with organisations at exactly this junction: AI readiness, governance design, safe-use training, and integration architecture for regulated and public-interest environments. Reduced rates are available for public interest and nonprofit organisations.
RO IT Systems (roitsystems.ca) works with organizations at exactly this junction: AI readiness, governance design, safe-use training, and integration architecture for regulated and public-interest environments. Reduced rates are available for public interest and nonprofit organizations.
References and Legal Basis
- Freedom of Information and Protection of Privacy Act, RSBC 1996, c.165 (FOIPPA), as amended by Bill 22-2021
- S.69: Privacy Impact Assessment requirements
- S.36.2: Privacy management program requirements
- S.36.3: Mandatory privacy breach reporting
- S.33.1: Cross-border data processing framework
- Part 5.1: Privacy offences and penalties (up to $50,000)
- Personal Information Protection Act, SBC 2003, c.63 (PIPA)
- Privacy Act, RSBC 1996, c.373
- Clarifying Lawful Overseas Use of Data Act (CLOUD Act), US Public Law 115-141 (2018)
- BC Ombudsperson Annual Report 2024-25 (released November 2025)
- BC Ombudsperson Letter to Minister Kahlon, March 26, 2025: Municipal integrity oversight
- City of Vancouver AI Advisory Committee (AIAC): terms and composition
- City of Vancouver Records Management By-law (VanRIMS framework)
- Microsoft M365 Blog, November 4, 2025: In-country Copilot processing announcement
- Microsoft On the Issues, December 9, 2025: $19B CAD Canadian investment commitment
- Microsoft M365 Blog, April 3, 2026 update: Timeline refinement for in-country processing
- Ken Sim, Mayor of Vancouver, verified public speech transcript, Telus sovereign AI data centre announcement, May 2026 (timestamp 49:29–55:43): https://www.youtube.com/watch?v=pO9i-8ug4RQ
- Implications of AI for Municipal Governance in BC, Ankita Goyal, October 2025
- BC Human Rights Code, RSBC 1996, c.210 (protected grounds including gender identity and expression)
- Trump Executive Order, “Defending Women from Gender Ideology Extremism and Restoring Biological Truth to the Federal Government,” January 20, 2025
- National Security Presidential Memorandum 7 (NSPM-7), “Countering Domestic Terrorism and Organized Political Violence,” September 25, 2025
- Heritage Foundation / Oversight Project, TIVE proposal, September 18, 2025 (advocacy document, not adopted US government policy)
- Global Affairs Canada, Travel Advisory for Canadians with “X” gender markers, updated October 2025
- Canadian Bar Association, “Canada’s Immigration Response for Trans Individuals,” submission to IRCC, 2025
- Canadian Bar Association, “Shifting Landscapes: Legal Justifications for Exceptional Immigration and Refugee Policies for Vulnerable Transgender Americans,” December 2025
- OIPC BC Strategic Plan 2025-28, “Trust in the Age of Information,” February 2026
- Ontario Human Rights Commission, Human Rights AI Impact Assessment framework
- Moffatt v Air Canada, 2024 BCCRT 149 (BC small claims tribunal, AI chatbot liability)
Analysis prepared May 2026. All regulatory citations verified against current BC law. Microsoft product availability reflects publicly announced commitments as of April 2026.
About the author: Morgane Oger is a technology leader and consultant with over 20 years of global experience in enterprise platforms and architecture. Her expertise includes machine automation, responsible AI, AI governance, and agentic AI readiness. Morgane Oger’s work has included trust audits of Microsoft’s Copilot and Copilot Studio, OpenAI’s ChatGPT, and Anthropic’s Claude services as well as proprietary AI solutions. Morgane Oger’s practice focuses on developing secure and compliant systems for regulated or sensitive environments (including compliance with PIPEDA and GDPR). MIT trained in AI governance and management, Morgane is the Founder and Director of RO IT Systems, a technology consultancy that works with public-interest and regulated organizations on AI readiness and governance. She is also a recognized public-interest leader and human rights advocate, with a long history serving on diverse non-profit boards including the Vancouver Pride Society, Atira Womens Resource Society, Trans Alliance Society, Vancouver DPAC,